Perfect Forward Secrecy Explained: Why Modern TLS Uses PFS
Perfect Forward Secrecy (PFS) is a property of a TLS connection that ensures past session traffic cannot be decrypted even if the server's long-term private key is later compromised. With PFS, each session uses a unique, ephemeral key that is discarded after the session ends. There is nothing to steal
Read more
How to Check for Viruses in Files Before Downloading
Checking if a file has a virus before downloading it is a crucial step in maintaining the security of your computer or device. Here are some methods to help you determine if a file may contain malware: Use Antivirus Software: Install reputable antivirus software on your computer or device. These
Read more
How to Digitally Sign App?
Digitally signing an app is a crucial step in the software development process, especially for ensuring the integrity and authenticity of the app. Here's a step-by-step guide on how to digitally sign an app: Step 1: Obtain a Code Signing Certificate: To digitally sign your app, you need a code
Read more
Understanding Checksums: The Foundation of Data Integrity Verification
A checksum is a value computed from data that lets you detect whether the data has changed. Think of it as a summary that is uniquely sensitive to any modification: if even one character in a file changes, the checksum changes completely. This makes checksums useful for verifying that a
Read more
Comprehensive Guide to OWASP’s Secure Coding Practices Checklist
As the frequency and sophistication of cyber threats continue to rise, secure coding practices have become essential for every software development project. The Open Web Application Security Project (OWASP) is a globally recognized authority in the field of application security. They provide invaluable resources and guidelines for building secure software,
Read more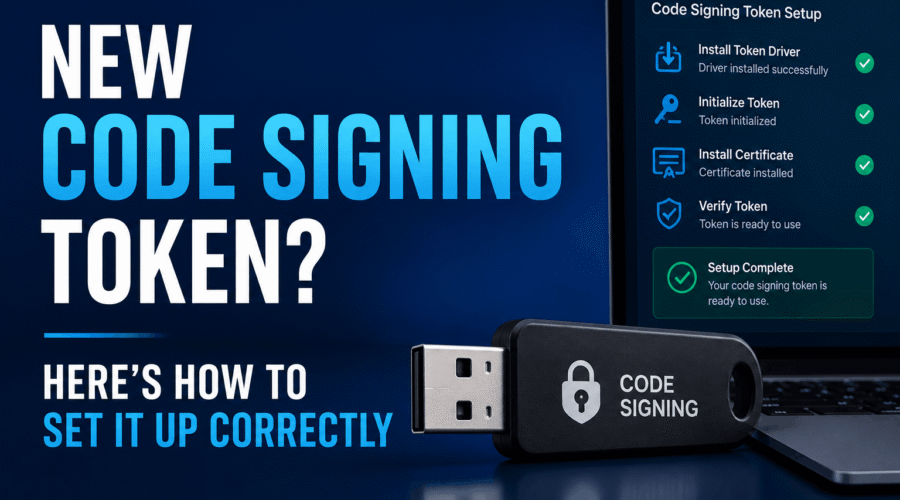
Setting Up a Code Signing Hardware Token for Secure Software Signing
Your code signing certificate has arrived on a USB hardware token. Since June 2023, this is how every commercially issued OV and EV code signing certificate is delivered (unless you chose a cloud HSM service): the private key is generated inside the token at the CA's facility and can never
Read more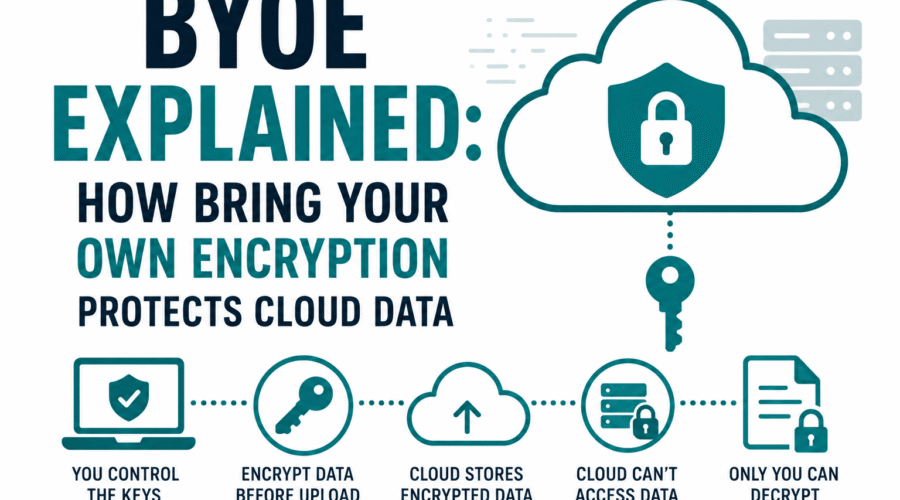
What Is BYOE? Understanding Bring Your Own Encryption in 2026
BYOE stands for Bring Your Own Encryption. It is a cloud security model in which the customer, not the cloud provider, supplies and controls the encryption used to protect their data in the provider's infrastructure. Instead of relying on the encryption keys the provider generates and manages, the customer deploys
Read more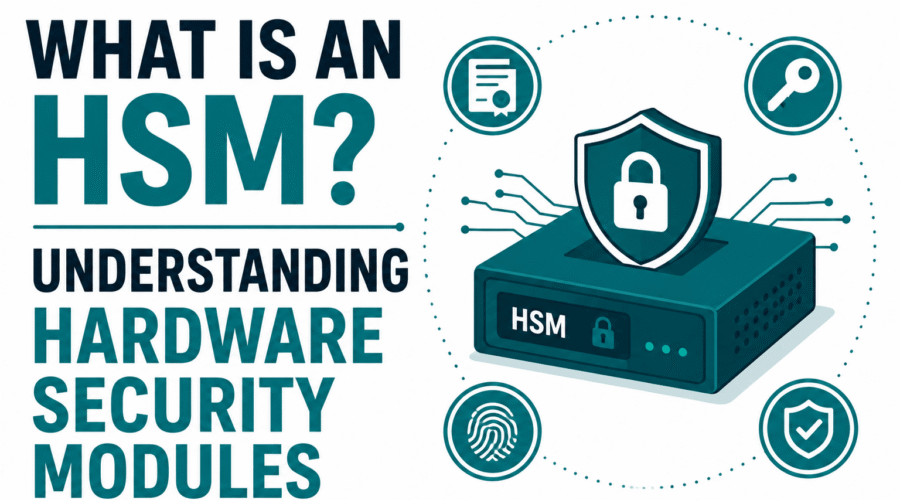
What Is an HSM? Understanding Hardware Security Modules
A Hardware Security Module (HSM) is a dedicated physical device built for one purpose: generating, storing, and using cryptographic keys in hardware that the keys can never leave. Every cryptographic operation involving a key stored in an HSM happens inside the device. Software sends data in, the HSM performs the
Read more
What Is PKI? Understanding Public Key Infrastructure and Digital Trust
This is the complete guide to Public Key Infrastructure (PKI). In this guide you will learn what PKI actually is, the five components that make it work, how a certificate gets issued and verified step by step, and why every HTTPS connection and every signed application on your computer depends
Read more
Runtime Application Self-Protection (RASP): Defending Your Apps in Real-Time
Runtime Application Self-Protection, commonly known as RASP, is a proactive cybersecurity approach designed to enhance the security of web and mobile applications. Unlike traditional security measures that focus on perimeter defense (like firewalls and intrusion detection systems), RASP operates within the application itself, monitoring and protecting it in real-time. How
Read more